Software quality governance for outsourced delivery teams, AI-generated code and AI features
Govern an outsourced team's quality by owning three things yourself: testable acceptance criteria for every story, a release readiness gate with named evidence, and a small set of delivery health metrics reviewed weekly. Delegate the practices to the vendor, but require proof from each one, including security checks and review of AI-generated code, before anything reaches your customers.
Book a solution review See the related serviceReviewed by David (CEO) · Updated 17 Sep 2026 · 16 min read
This guide is for founders, CTOs, product owners and procurement leads who work with an outsourced or offshore development team and remain accountable for what it ships. It explains how to split quality responsibilities between buyer and vendor, how to write acceptance criteria that can be tested, how to fold security into those criteria, how to govern AI-assisted engineering and test AI features, how to run a release readiness gate, which delivery health metrics to watch, and what a governance cadence looks like in practice.
In this guide
- Who owns quality when delivery is outsourced
- Acceptance criteria that can be tested
- Security as acceptance criteria
- AI-assisted engineering: govern the output, not the tool
- Testing AI features
- A release readiness gate
- Delivery health metrics that are hard to game
- A governance cadence that works across time zones
- An example from print commerce
- Trade-offs and common mistakes
- A quality governance checklist
- Planned guides in this cluster
- Limitations of this guide
- Frequently asked questions
- How this guide was made
- Next step
Who owns quality when delivery is outsourced
Outsourcing moves the work, not the accountability. Customers, regulators and your board judge your product, whoever wrote the code. Good governance therefore separates what the buyer must decide from what the vendor should be trusted to do, and asks for evidence at each boundary.
| Area | Buyer decides | Vendor delivers | Evidence to ask for |
|---|---|---|---|
| Scope and priorities | What matters, in what order | Estimates, risks and options | A backlog with acceptance criteria |
| Acceptance | What "done" means for each story | Tests that prove it | Test results linked to criteria |
| Security | Risk appetite, data classes, compliance needs | Secure coding, reviews and scanning | Review records, scan reports, fixed findings |
| Release | Go or no-go, and when | Release candidate, notes and rollback plan | A readiness checklist signed by both sides |
| Operations | Support hours and priority rules | Monitoring, incident handling and fixes | Incident log and post-incident reviews |
| Knowledge | What must be documented and transferred | Documentation and code in your repositories | Repository access, architecture notes, runbooks |
| AI use | Which AI tools may see code and data | Human review of AI-generated code and tests | An approved tool list and review records |
The split holds whatever the engagement model. What changes between a fixed-scope project and a dedicated team is who carries the estimation risk, not who is accountable for quality.
Acceptance criteria that can be tested
Most quality disputes with an outsourced team begin with a story that both sides read differently. Acceptance criteria prevent that when they are specific enough that a tester who never attended the planning meeting could decide pass or fail.
A practical format is: given a starting situation, when the user does something, then a result is visible. For example: given a signed-in customer with two saved addresses, when they check out, then both addresses are offered and the default one is preselected; and if the payment fails, the order stays in the basket and a clear error message is shown.
Good criteria share five traits:
- Observable. They describe behaviour a person or an automated test can see, not intentions.
- Bounded. They state limits, such as file sizes, the response times you care about, and supported browsers or devices.
- Failure cases included. They say what happens when something goes wrong, not only on success.
- Data named. They list the roles, records and edge cases needed to test the story.
- Non-functional needs stated. Accessibility, performance and security needs appear in the criteria or in a shared definition of done, not in a separate document nobody reads.
Pair story-level criteria with a definition of done that applies to every story: code reviewed, automated tests added and passing, security checks run, documentation updated, and the change deployed to a test environment the buyer can use. The definition of done is where quality stops depending on individual effort.
Approve criteria before a story enters a sprint, not during testing. A story without approved criteria is not ready to start, however urgent it looks.
Security as acceptance criteria
Security fails in outsourced delivery when it is a phase at the end rather than a set of requirements from the start. Two public frameworks help buyers state requirements without writing them from scratch.
- OWASP Application Security Verification Standard (ASVS). OWASP describes the ASVS as a basis for testing the technical security controls of web applications, as a list of requirements for secure development, and as something that can be used in procurement contracts. Version 5.0.0 is the current stable release. Buyers can select the requirements that match their risk and reference them in acceptance criteria.
- NIST Secure Software Development Framework (SSDF), SP 800-218. The SSDF groups secure development practices into four areas: prepare the organization, protect the software, produce well-secured software, and respond to vulnerabilities. It gives buyers a shared vocabulary for asking how a vendor works, not only what it ships.
In practice, ask the vendor to show, for each release, which security requirements were in scope, how the code was reviewed, which scans ran and what they found, which findings were fixed, and which were accepted as risks and by whom.
Netbase's published security practices are secure code review and version control, TLS in transit and AES at rest, role-based access control, MFA for admin dashboards, vulnerability scanning and penetration testing, and disaster recovery; NDAs, DPAs and SLAs are available on request, and contributors work under NDA. Netbase holds ISO 27001 certification for information security management and a SOC 2 Type II attestation. It follows GDPR alignment for data privacy in Europe, HIPAA-aligned methodologies for healthcare data handling, and CCPA compliance practices for clients with U.S. customer bases. These apply to Netbase's own operations and working practices. They do not certify a client's product or hosting, and your own compliance still needs its own assessment.
AI-assisted engineering: govern the output, not the tool
Most outsourced teams now use AI assistants to draft code, tests and test data. Banning them is rarely realistic, and trusting them blindly is worse. Govern what they produce, with the same evidence you ask for any other change.
AI helps quality work in useful ways: drafting test cases from approved acceptance criteria, generating synthetic edge-case data instead of copying production records, grouping failing tests and duplicate defect reports, and flagging risky changes before human review. Each is a draft that a named engineer or tester accepts.
The risks are specific, so the controls can be too:
- Tests that confirm the code instead of the requirement. Tests generated from the code pass by construction. Require tests to trace to acceptance criteria, and review them as carefully as the code.
- Plausible but insecure code. Generated code can repeat outdated or unsafe patterns. Keep secure code review and scanning in the definition of done for every change, whoever or whatever wrote it.
- Data sent to the wrong place. Agree which AI tools are approved, and that your code, secrets and personal data never go to tools outside that list or to models that train on them.
- Unclear accountability. The engineer who merges a change answers for it. "The AI wrote it" is not an accepted risk.
Add one line to the definition of done: AI-generated code and tests reviewed and approved by a named person.
Testing AI features
An assistant, classifier or recommendation feature does not give the same answer to the same input every time, so pass-or-fail criteria need a different shape. Acceptance becomes a measured result on an agreed evaluation set.
-
Answer quality
Score a fixed, versioned set of real cases; agree the pass threshold before build
-
Escalation
Out-of-scope or low-confidence requests hand over to a person
-
Data boundaries
Prompts that try to extract other users' data or bypass instructions fail
-
Actions
Anything that changes records, prices or money waits for human approval
-
Cost and latency
Calls per request and response time stay within agreed limits
-
Regression
The evaluation set runs again whenever the model, prompt or retrieved data changes
Record the model and prompt version with every release, because a provider's model update can change results without a line of your code changing.
A release readiness gate
A release readiness gate is a short meeting or checklist that decides whether a release candidate goes to customers. Its value lies in naming the evidence in advance, so the decision is not made on confidence alone.
-
Scope
- Evidence
- Release notes listing stories and known issues
- Who signs
- Product owner
-
Functional quality
- Evidence
- Acceptance tests and the regression suite passing
- Who signs
- QA lead
-
Security
- Evidence
- Scan results reviewed; open findings accepted by a named owner
- Who signs
- Security owner or CTO
-
Performance
- Evidence
- Key journeys measured against agreed limits
- Who signs
- Tech lead
-
Data and migrations
- Evidence
- Migration rehearsed on a copy; backup taken
- Who signs
- Tech lead
-
Rollback
- Evidence
- A tested rollback, or a feature flag to switch the change off
- Who signs
- Release manager
-
Operations
- Evidence
- Monitoring and alerts in place; support team briefed
- Who signs
- Operations owner
-
AI features
- Evidence
- Evaluation results against the threshold; model and prompt versions recorded
- Who signs
- Product owner and AI lead
-
Communication
- Evidence
- Customer-facing notes ready where needed
- Who signs
- Product owner
Keep the gate proportionate. A small fix can pass on automated evidence; a release that migrates data or changes checkout deserves the full list. Record every gate decision, including releases that went out with accepted risks, so trends are visible later.
Delivery health metrics that are hard to game
Metrics help buyers see a delivery problem before it becomes a missed launch. They do harm when they become targets that a team optimizes at the expense of the product.
DORA's research programme defines five software delivery performance metrics: change lead time, from a commit to its deployment in production; deployment frequency; failed deployment recovery time; change fail rate, the share of deployments that need immediate intervention; and deployment rework rate, the share of deployments that are unplanned and caused by a production incident. Together they balance speed against stability, which makes them harder to game than any single number.
-
Change lead time
- What it tells the buyer
- How quickly a finished change reaches users
- Watch for
- Long waits in review or testing queues
-
Deployment frequency
- What it tells the buyer
- Whether releases are small and routine
- Watch for
- Big, rare releases that bundle risk
-
Change fail rate
- What it tells the buyer
- How often releases cause trouble
- Watch for
- Rising rates after deadline pressure
-
Failed deployment recovery time
- What it tells the buyer
- How quickly problems are undone
- Watch for
- Manual, slow rollbacks
-
Deployment rework rate
- What it tells the buyer
- How much work is unplanned firefighting
- Watch for
- Incident-driven releases crowding out planned work
-
Escaped defects
- What it tells the buyer
- Defects found by users rather than by tests
- Watch for
- Gaps in acceptance criteria or test data
-
Predictability
- What it tells the buyer
- Committed work delivered per iteration
- Watch for
- Chronic overcommitment
-
AI evaluation trend
- What it tells the buyer
- Whether AI features hold quality across model and prompt changes
- Watch for
- Silent drops after a provider update
The last three rows are common additions, not DORA metrics. Review trends rather than single values, and read the metrics together. A team that deploys often but fails often is not healthy; neither is one that never fails because it rarely releases. Never compare vendors or teams on raw numbers without the context of product, architecture and risk.
A governance cadence that works across time zones
Cadence turns metrics and gates into decisions. Netbase's published governance model includes weekly reviews, KPI dashboards, a dedicated account manager and project manager, Slack or Zoom for day-to-day communication, and client dashboards. Its delivery lifecycle has six steps: discovery and strategic alignment; team assembly and architecture planning; agile execution with outcome-based milestones; modular and productized components; training, rollout and optimization; and ongoing support and co-building. Teams range from 3 to 30 people and combine business analysts, project managers, solution architects, developers, QA and UI/UX designers; work typically starts within 1 to 2 weeks after discovery. Support coverage runs Monday to Saturday, with Sunday off, and delivery communication is in English. AI tools are chosen per project and agreed with the client.
A cadence buyers can adapt:
| Rhythm | Purpose | Inputs |
|---|---|---|
| Daily, in writing | Unblock work | Short updates and open questions |
| Weekly review | Check progress, quality and risks | Demo, metrics dashboard, risk list |
| Per release | Decide go or no-go | Readiness gate evidence |
| Monthly or quarterly | Adjust scope, team and priorities | Metric trends, budget, roadmap |
| After incidents | Learn without blame | Timeline, cause, actions with owners |
For the testing and quality practices behind this cadence, see Netbase's quality engineering and testing service.
An example from print commerce
Quality governance matters most where a defect costs a sale. In print commerce, a customer often designs a product online, approves a proof and pays in a single session, so a broken editor, a slow page or a failed payment ends the order. That is why web-to-print platforms need acceptance criteria for design, proofing and checkout journeys, not only for back-office screens, and why the printing and packaging industry is a demanding place to practise release discipline.
USticker. For USticker, Netbase delivered an e-commerce payment enhancement engagement. The published results are conversion up 40% for users of the design tool, completed designs up 32% in six months, retention up 25%, online-order revenue up 15% and page load time down 21%. The figures describe the engagement as a whole, as reported for that client, and the 40% applies only to users of the design tool. They show which measures a release gate for a commerce product should protect: conversion, completion and speed.
Plan the next step with a Netbase consultant
Trade-offs and common mistakes
- Too many gates. Heavy approval for every change slows delivery and pushes teams to batch risky releases together. Scale the gate to the change.
- Metrics as targets. Paying or ranking a team on deployment counts or defect counts invites gaming. Use metrics to ask better questions.
- Security left to the end. A penetration test in the week before launch finds problems too late to fix well. Put requirements into the criteria.
- Acceptance by demo only. A good demo shows the happy path. Ask for tests that cover failure cases too.
- Vendor-only repositories. If the code and pipelines live only in the vendor's accounts, governance depends on goodwill. Keep them in yours.
- Changing criteria after the build without saying so. Late changes to acceptance criteria are normal, but they are scope changes; record them as such so estimates and quality are judged fairly.
- No named owner for accepted risks. Every open finding shipped to production needs a person who accepted it and a date to revisit it.
A quality governance checklist
- Every story has testable acceptance criteria, including failure cases.
- A shared definition of done covers review, tests, security checks and documentation.
- Security requirements reference a public standard such as the OWASP ASVS.
- The vendor can explain its practices against a framework such as the NIST SSDF.
- A release readiness gate names its evidence and who signs each item.
- Rollback is tested, not assumed.
- Delivery health metrics are tracked as trends and reviewed weekly.
- Code, pipelines and documentation live in repositories you control.
- Support hours, priority rules and escalation contacts are written down.
- Incidents lead to blameless reviews with owned actions.
- AI-generated code and tests are reviewed by a named person, using approved tools only.
- AI features are accepted against a versioned evaluation set, re-run on every model or prompt change.
Planned guides in this cluster
This pillar anchors deeper guides now being planned: a software quality engineering strategy for outsourced delivery; security questions to ask a software development partner; an acceptance criteria and release readiness checklist; and how to measure engineering delivery health. Until they are published, the sections above cover the essentials.
Limitations of this guide
This is practical guidance from Netbase delivery experience, not original research or legal advice. OWASP, NIST and DORA are cited as public frameworks, not as conformance claims. The AI sections describe current practice in a fast-moving area, not measured results. Netbase's security practices are described as practices, with no claim about the effectiveness of any control, and its certifications apply to Netbase's own operations. The USticker results were reported for that engagement as a whole and depend on the client's baseline and market.
Frequently asked questions
The buyer owns them. A vendor business analyst can draft them, but the product owner approves each one before work starts.
You need someone on your side who can judge acceptance. That can be a product owner with time for it; larger programmes often add an independent QA lead.
Change lead time, deployment frequency, change fail rate and failed deployment recovery time, plus escaped defects. Add others once these are trusted.
No. It covers the vendor's own information security management; your product still needs its own security requirements and testing.
Agree a versioned evaluation set of real cases and a pass threshold before the build, test escalation and data boundaries separately, and re-run the set whenever the model or prompt changes.
Progress against the plan, a demo link, delivery metrics as trends, open risks with owners, open security findings, and the decisions needed from you, with dates.
Weekly for progress and quality, at every release for go or no-go, and quarterly for trends and team shape.
How this guide was made
The Netbase Editorial Team wrote this guide from Netbase's published delivery, governance and security pages, the USticker case study and public guidance from OWASP, NIST and DORA. David (CEO) reviewed every Netbase fact. External sources are cited with access dates. Drafting used AI assistance (Claude). Its purpose is to help buyers stay accountable for quality while the work itself is outsourced.
Next step
Share how your outsourced delivery is governed today, the releases that worry you and any compliance needs, and we will book a solution review to set out acceptance, release and metric practices that fit. You can also see the related service or browse more Netbase insights.
Work behind this guide
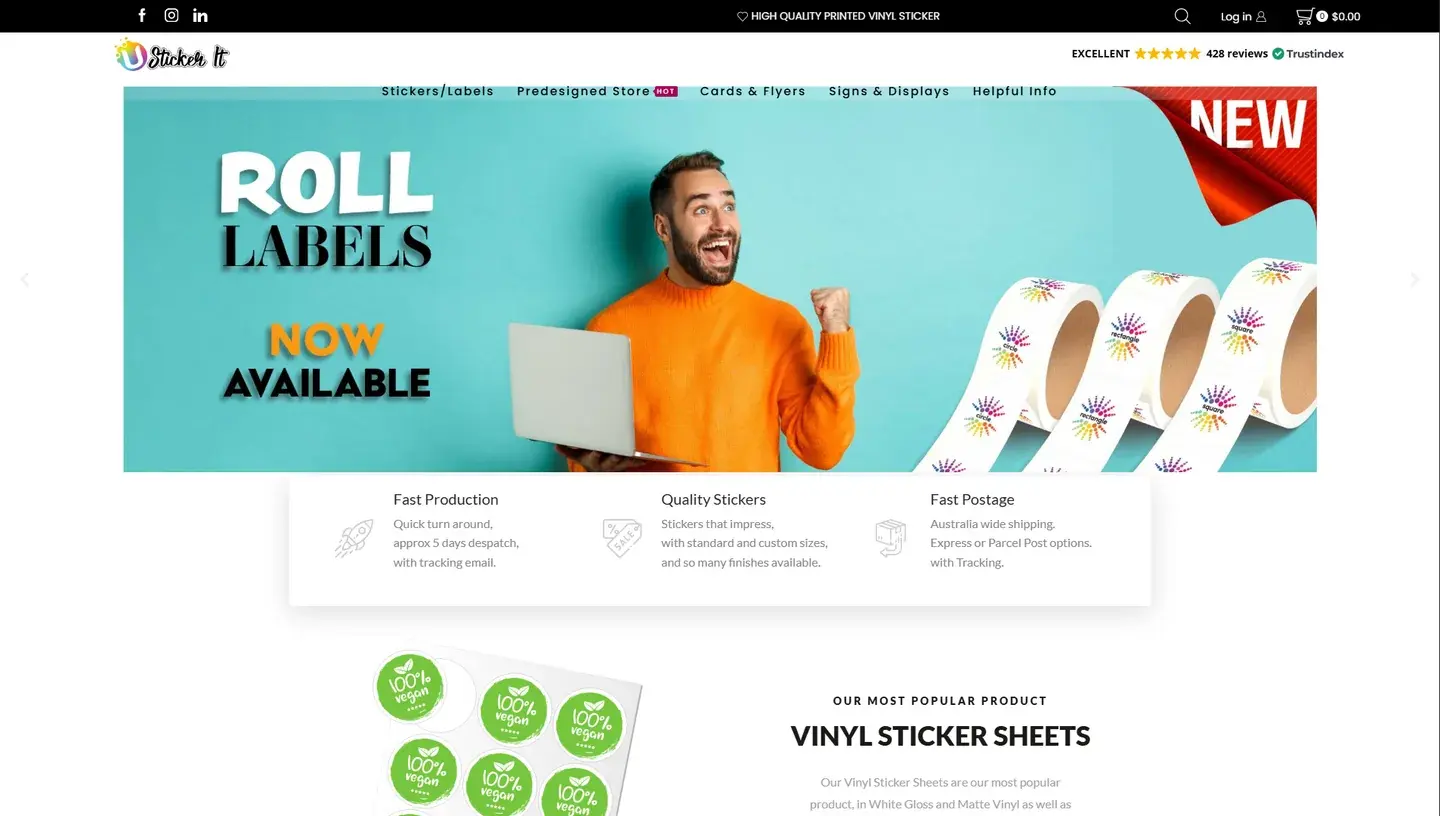
Design-tool users converted 40% more often; online-order revenue rose 15%.
Keep ReadingRelated services and solutions
 AI-assisted QA and software testing that run inside delivery
Netbase provides software testing and QA services for product and commerce teams to release often without breaking what customers use. QA runs inside delivery, not after it: acceptance criteria, automated regression with AI-generated test drafts, performance budgets and release readiness checks. Page speed shows the result: USticker's page load fell 21%, and PrintLeo's improved 35%.
Learn More
 Web-to-print platform with AI design assistance, from online design to a print-ready order
A web-to-print platform is an online ordering, design and prepress workflow that helps print businesses sell custom products: customers configure, design and approve their order online, AI can suggest layouts and catch artwork problems, and production receives a print-ready file. Netbase has delivered 50+ custom web-to-print platforms across apparel, packaging, signage, promotional merchandise and corporate B2B portals.
Learn More
Discuss a project
Netbase JSC helps organizations design, build, modernize, and operate digital products and AI-enabled business systems.+84 937 869 689
91 Nguyen Chi Thanh, Dong Da, Hanoi, Vietnam
Get in touch
Tell us what you want to build, modernize, or operate.