Application security assurance for web, SaaS and AI features
Netbase provides application security testing for product and engineering leaders to find and fix vulnerabilities before release, including in AI features. We review code with AI-assisted triage, scan dependencies and test running applications, then rank findings and retest fixes. Netbase's own ISO 27001 certification and SOC 2 Type II attestation cover Netbase's operations, never your application.
Book a solution review View relevant workReviewed by David (CEO) · Updated 17 Sep 2026
Shipping a release that handles customer data? Book a solution review.
What application security assurance includes
Most breaches start with ordinary faults: a missing access check, an outdated library, a secret in the code, an unvalidated input. Application security assurance looks for those faults in the code, in its dependencies and in the running system, and helps your team fix them. It sits in our Quality & Security family.
Included
- Secure code review of the paths that matter most
- Dependency and supply-chain scanning
- Vulnerability scanning of applications and APIs
- Penetration testing of web applications and APIs
- Access control, authentication and MFA review
- Testing of AI features for prompt injection and data leakage
- Remediation support and retesting
- Recovery and hardening of compromised stores
Not included
- Certifying your product, hosting or company
- Formal audit or attestation reports
- Round-the-clock security monitoring
- Physical and network perimeter testing
- Legal opinions on regulatory compliance
When to use it, and when another route fits
Security testing pays off when a fault would expose customer data, money or trust.
Good fit
- A SaaS or commerce platform before a major release
- An application that stores personal or payment data
- A product adding AI features that read company data
- Customers asking for evidence of secure development
Another route fits better
- A brochure site with no logins or customer data
- You need a certificate for your company: that is an audit by a certification body
- The application will be replaced within weeks
- No team is available to fix what is found
Every route is listed in the services directory.
Outcomes and buyer jobs
Product and engineering leaders hire security assurance to:
Findings are ranked by impact and likelihood, not listed by tool output.
Each finding comes with the fix path, and fixes are retested.
You can show which practices ran on which release.
Prompt injection and data leakage are tested before launch.
Capability modules and deliverables
The assets, users, data flows and threats that decide where to test
Findings with code locations and fix guidance
Vulnerable and unmaintained libraries, ranked by reachability
Automated scans of applications and APIs, with false positives removed
Manual tests of authentication, access control and business logic
Prompt injection, data leakage and tool-misuse test cases
A prioritised report, a fix review with your developers and a retest
Delivery process, team and governance
Security work follows our six-step delivery lifecycle:
-
Discovery and strategic alignment
We agree the scope, the environments and the rules of engagement in writing.
-
Team assembly and architecture planning
Reviewers read the architecture and data flows before any test runs.
-
Agile execution with outcome-based milestones
High-risk areas are tested first, and critical findings are reported as soon as they are confirmed.
-
Modular and productized components
Repeatable checks run from maintained checklists and scanners.
-
Training, rollout and optimization
Developers get a walkthrough of each finding class and how to avoid it.
-
Ongoing support and co-building
Checks can move into your release pipeline so they run on every change.
The practices we apply are the ones Netbase uses in its own delivery: secure code review and version control, TLS in transit and AES at rest, role-based access control, MFA for admin dashboards, vulnerability scanning and penetration testing, and disaster recovery. NDAs, DPAs and SLAs are available on request, and every contributor works under NDA. We use the OWASP Application Security Verification Standard (ASVS), version 5.0.0 of May 2025, as the baseline for which controls to verify. Teams range from 3 to 30 people across analysis, development, QA and architecture, work typically starts within one to two weeks after discovery, and governance includes weekly reviews and a dedicated account manager and project manager. Reviews run remote-first, and for products we build, security by design starts in the first sprint rather than at a pre-release test.
Netbase holds ISO 27001 certification and a SOC 2 Type II attestation, and follows GDPR alignment, HIPAA-aligned methods and CCPA practices. These describe how Netbase runs its own operations. They do not extend to your application or hosting, and this service does not issue a certificate.
AI in this service
AI changes security work on both sides. As a tool, AI-assisted code review and dependency triage help reviewers read large codebases faster and sort scanner output; a human reviewer confirms every finding, and no AI output closes a finding on its own. As a target, AI features bring new risks. The OWASP Top 10 for LLM Applications (2025) lists prompt injection first, followed by sensitive information disclosure, and also covers excessive agency and system prompt leakage. We test for those where your product lets a model read company data or call tools.
-
Available capability
AI-assisted code review and dependency triage
A delivery practice with human confirmation; not yet tied to a published security case.
-
Available capability
Security testing of generative AI features
Part of the AI capability areas Netbase offers; not yet tied to a published security case.
Engagement models and commercial variables
Most Netbase projects are delivered on fixed-price contracts agreed after discovery, and a scoped assessment fits that model well. Continuous checks for a product with frequent releases can run on a monthly team retainer, and milestone-based and KPI-linked terms are also offered. We do not publish rate cards.
What moves effort and cost: the size and age of the codebase, the number of roles and integrations, whether AI features are in scope, how many environments must be tested and how quickly fixes are ready for retest.
Technology as an implementation choice
We test the stack you run. Most applications we review use the frameworks compared on our backend platforms page, each with its own common faults. Findings point to the framework's safe patterns, so your team fixes the class of fault, not only the instance.
Technologies we build with
Industry applications
Printing and packaging. Web-to-print stores accept uploaded artwork, run design tools in the browser and pass orders to production. File uploads, payment flows and partner integrations are the areas we test first.
SaaS products. Multi-tenant platforms must keep each customer's data apart. Tenant isolation, role checks and API authorisation are the core of the review, and our SaaS product accelerator builds these controls in from the start.
 Printing and packaging: online ordering, AI artwork checks and production handoff
Netbase helps print and packaging businesses move ordering, artwork approval and production handoff online, with AI where files go wrong, so customers configure, design, proof and pay in one flow and the press floor receives clean jobs. Six published print-commerce case studies and 50+ custom web-to-print platforms, across apparel, packaging, signage, promotional merchandise and B2B portals, back this page.
Learn More
Proof: SaaS platforms Netbase builds and runs
Evidence maturity: application security assurance is a growth capability. The records below are platforms Netbase builds and runs through its Business Divisions; they show the kind of application this service reviews. No stand-alone security engagement, and no test result, is published.
Printcart (Netbase Business Division). A web-to-print and print-on-demand platform that turns online orders into print-ready files and routed fulfillment, running on merchants' own stores or as Shopify, Wix and WooCommerce apps. See the Printcart record.
Cloodo (Netbase Business Division). An AI-powered digital workplace where internal staff and outsourced specialists share company profiles, services and projects, which makes access control central. See the Cloodo record.
Security recovery for a compromised Magento store (client not named). For an existing client store Netbase had built, Netbase scoped a three-phase recovery: investigation and a malware scan of code, database and server with an infected-file report; cleanup of malware and backdoors with core files restored; then repair of damaged modules and themes, Magento security patches and hardening. The typical range is 6–13 days depending on the damage, and how much can be restored is confirmed after the scan.
More projects are in our work.
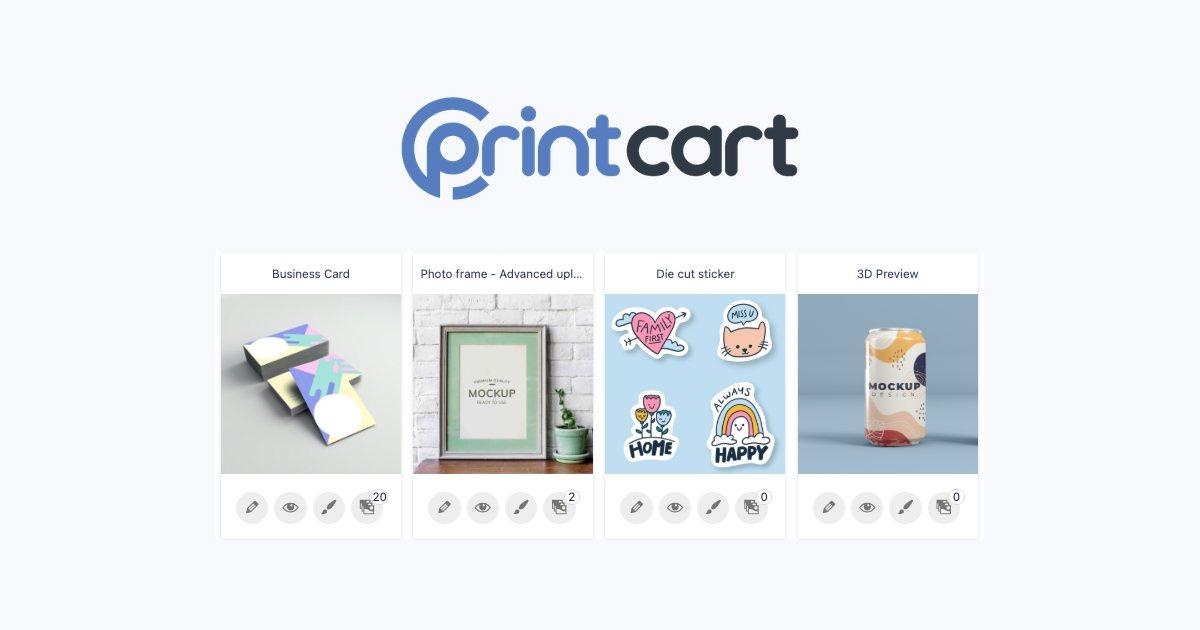
Netbase designed, engineered and operates the multi-tenant platform: an online design studio, automatic print-ready files, print order management, and store apps plus an API that plug into any storefront.
Keep Reading
It puts company profiles, service listings, projects, tasks and team collaboration in one cloud workspace, beside CRM, HRM, Cloud ERP and AI modules, for internal staff and outside specialists alike.
Keep ReadingBuyer FAQ
No. Netbase's ISO 27001 certification and SOC 2 Type II attestation cover Netbase's own operations. A certificate for your product comes from an audit by a certification body.
Only the named reviewers, all under NDA. NDAs and DPAs with your company are available on request.
It depends on codebase size, roles and integrations. Scope, environments and dates are agreed before testing starts.
Your developers can fix it with our guidance, or Netbase developers can deliver the fixes. Either way, fixes are retested.
Often, yes. We investigate and scan first, then clean and restore, then patch and harden; for a compromised Magento store the typical range is 6–13 days. Recovery is scoped after the scan, never promised before it.
No. AI-assisted triage runs only with tools and settings agreed with you in the rules of engagement, and a human reviewer confirms every finding.
In English, through weekly reviews and a named project manager. Critical findings are reported as soon as they are confirmed.
Testing once and stopping. Security checks work best in the release pipeline, where every change is reviewed.
Related solutions
 SaaS product accelerator: launch an AI-ready SaaS on proven Netbase modules
A SaaS product accelerator is a set of reusable Netbase modules for accounts, billing, roles and integrations that helps founders and product teams launch subscription software faster, with room for in-product AI from the first release. Reusing these productized modules can cut development time by up to 60%, and the approach is proven on Printcart, the web-to-print SaaS Netbase built and operates.
Learn More
Service owner and next step
This service is owned by David, Netbase's Chairman, founder and CEO, and maintained by the Netbase Editorial Team. Want to know what an attacker would find first? Book a solution review, or view relevant work first.
Discuss a project
Netbase JSC helps organizations design, build, modernize, and operate digital products and AI-enabled business systems.+84 937 869 689
91 Nguyen Chi Thanh, Dong Da, Hanoi, Vietnam
Get in touch
Tell us what you want to build, modernize, or operate.